What is YARA? Preparing a YARA Rule for the Zeus Botnet
In this article, I'll try to explain what a YARA rule is and how a YARA rule is written, using the Zeus Botnet malware as an example. Happy reading. :) What is YARA?…
Hello everyone, in this article I’ll try to explain what a YARA rule is and how a YARA rule is written, using the Zeus Botnet malware as an example. Happy reading. :)
What is YARA?
YARA is a tool that aims to help detect, identify, and classify malware in the fastest and best way possible. It’s an open source resource developed by VirusTotal.
You can download YARA’s executable and run it on your own system as well. You can download the latest version from http://plusvic.github.io/yara/.
Writing a YARA Rule
YARA rules are rules created to help classify malware and identify the hex values of that malware’s code. When we add the rules we write to our intrusion detection systems, we can easily eliminate malware trying to infiltrate the system using the YARA rule we prepared beforehand. Thanks to these YARA rules, we protect ourselves from the damage that the malware we wrote the YARA rule for would otherwise cause to our system.
Each YARA rule definition consists of a set of logical expressions. I’ve discussed these expressions below; here I took the Zeus Botnet malware as my example and explained the writing of a YARA rule in a simple way.
The basic logic of a simple YARA rule is as follows:
rule rule_name
{
        meta:

        authour= "Mehmetkadir"

        decription="x\_yararule"

        strings:

        $a ="malware"

        $b="yara rules"

        condition:

        $a and $b
}
- My aim here will be to detect the distinctive characteristics of the Zeus Botnet itself and prepare a YARA rule accordingly.
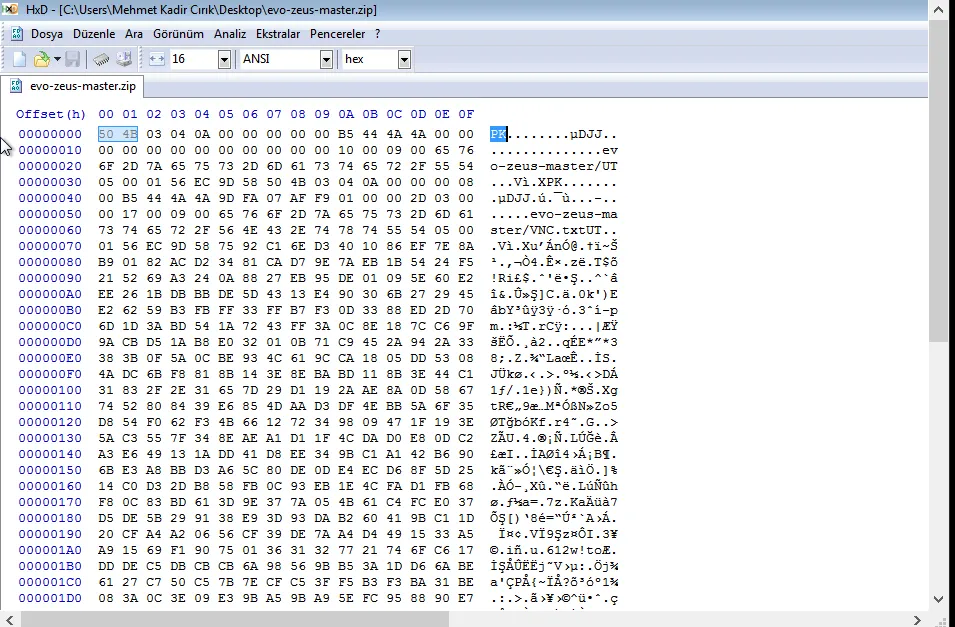
First, I installed HxD on my virtual Windows 7 machine and ran it, then I downloaded the Zeus Botnet file and loaded this file into HxD.
- In this part, the PK value came up first, and I thought this might be something significant, so I wanted to add it into the YARA rule.
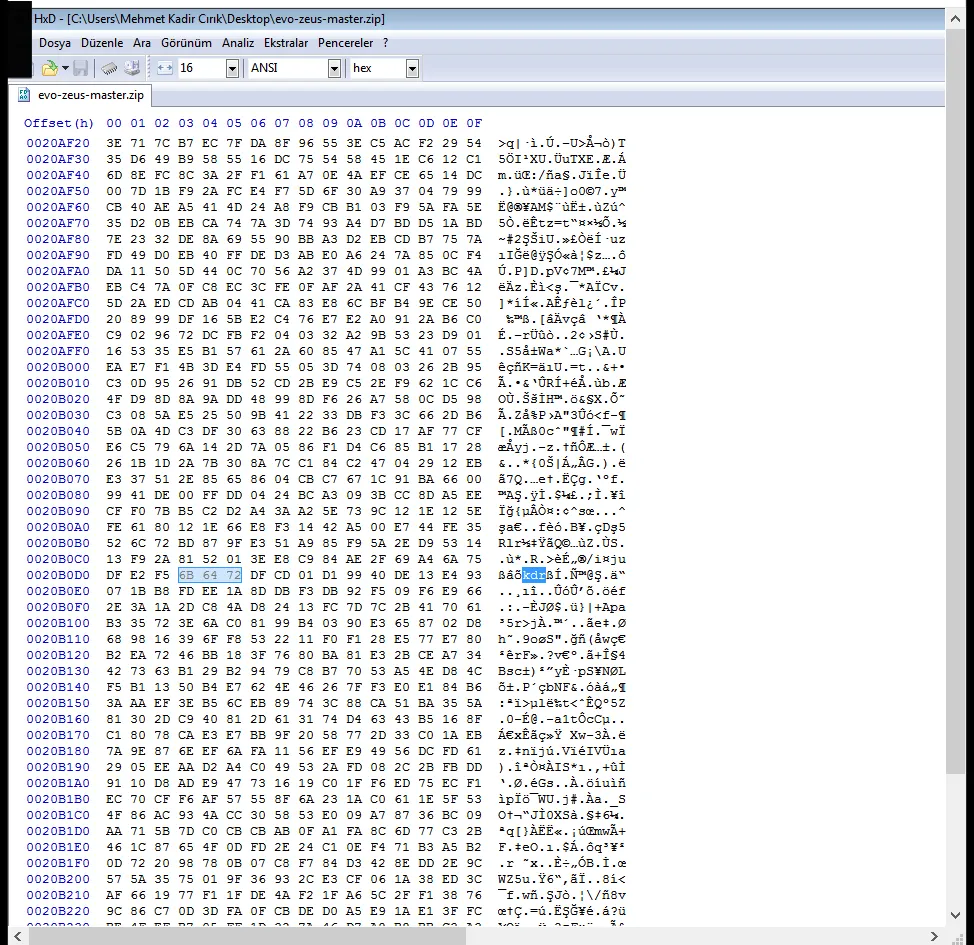
- In this part, I thought the kdr string might be significant for me, and I wanted to add this to the YARA rule as well.
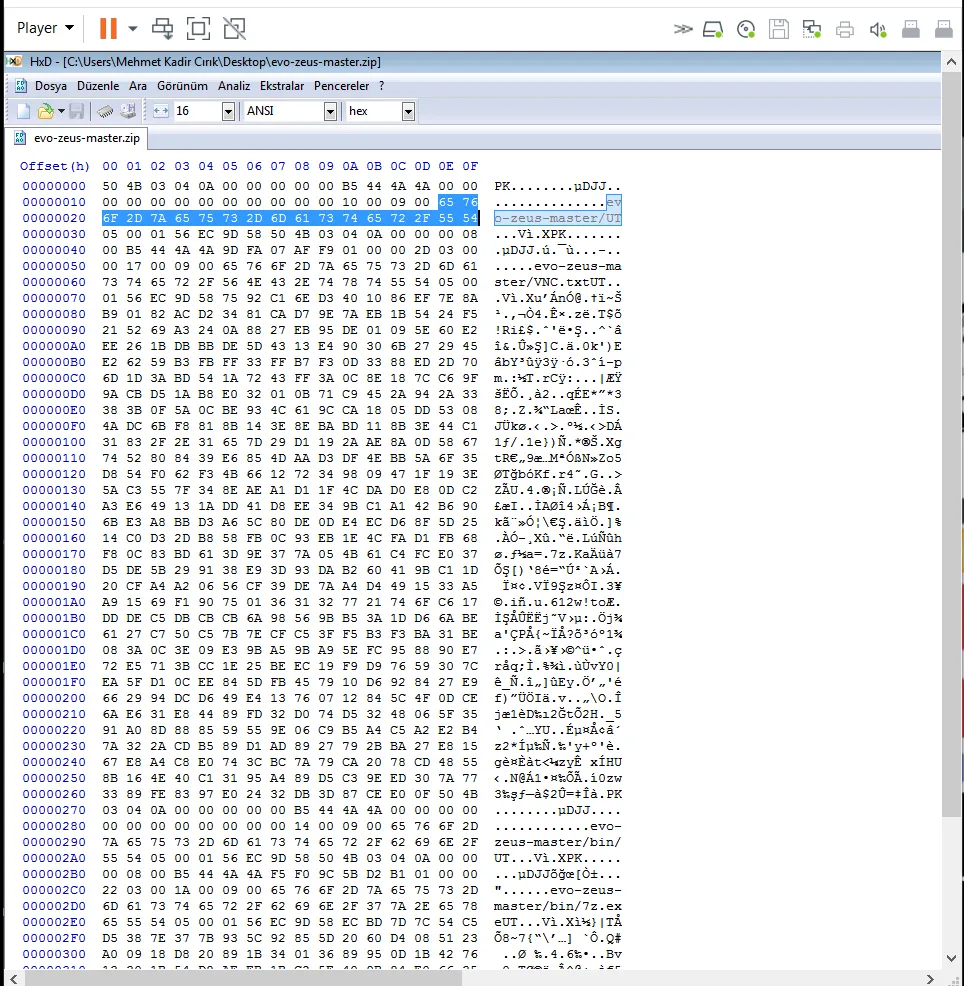
- The string expression here caught my attention, and after a bit of research, I concluded that it was the source code of the Zeus Botnet using Tor.
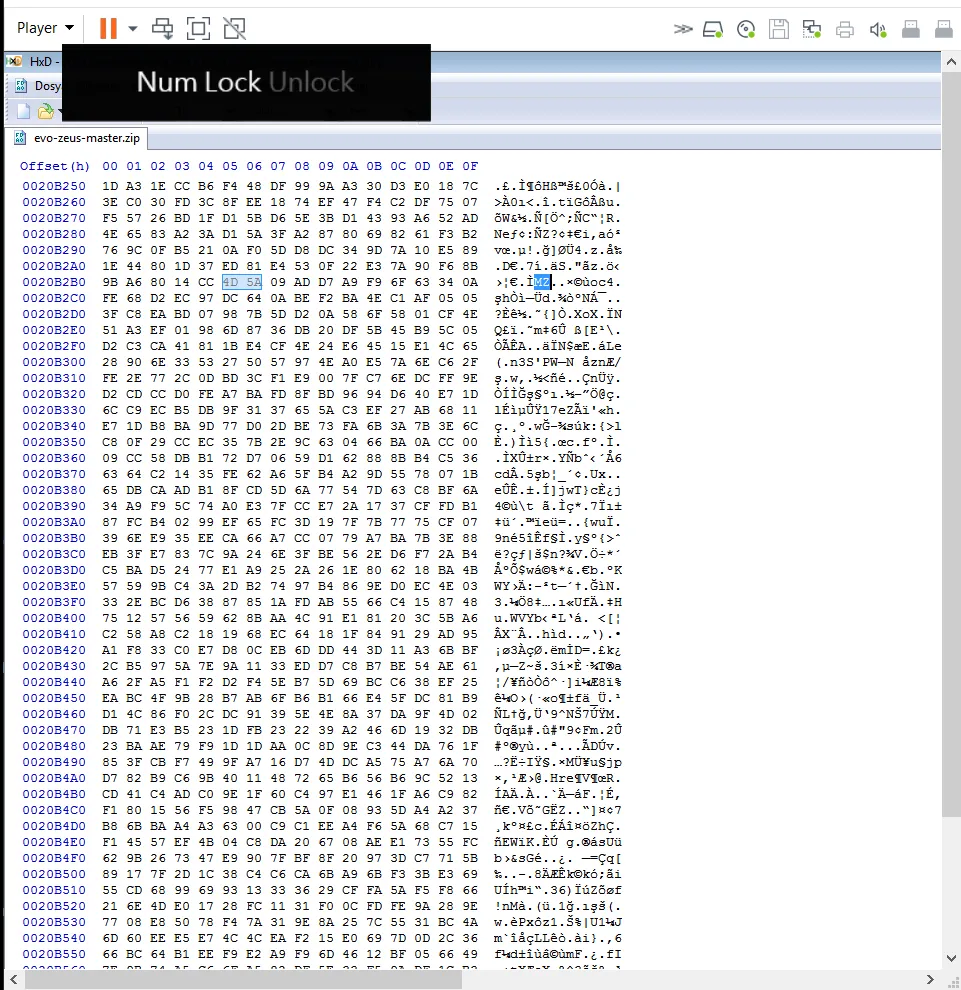
- In this part, I also came across the string value MZ. MZ indicates that it’s a standard Windows executable file.
And here’s a brief summary of the YARA rule I ended up preparing. First, I gave the YARA rule a name. Then I added the PK, kdr, the string expression for the source code on the Tor network, and the MZ value into my YARA rule. Finally, in the condition section, I decided that it should raise an alert if all 4 of these expressions are encountered at the same time. Of course, you can make changes here to suit your own needs, and adjust the YARA rule you write accordingly.
rule zeusbotnet_yara #rule
{
meta:
decription=“zeusbotnet_yara” #description
author=“Mehmet Kadir CIRIK” #author
strings:
$a ={50 4B} #PK
$b ={6B 64 72} #kdr
$c ={65 76 6F 2D 7A 65 75 73 2D 6D 61 73 74 65 72 2F 55 54}
$mal=“MZ”
condition:
$a and $b and $c and $mal
}
Thanks for reading this far. :)